GHOST
Learn security by replaying real breaches.
GHOST turns public incident reports into hands-on command-building challenges. On the Red track you rebuild the commands the attackers actually ran. On the Blue track you rebuild the response defenders should have run. You learn real tools, real syntax, and real attack chains, not quiz trivia.
App Store launch planned · December 2026
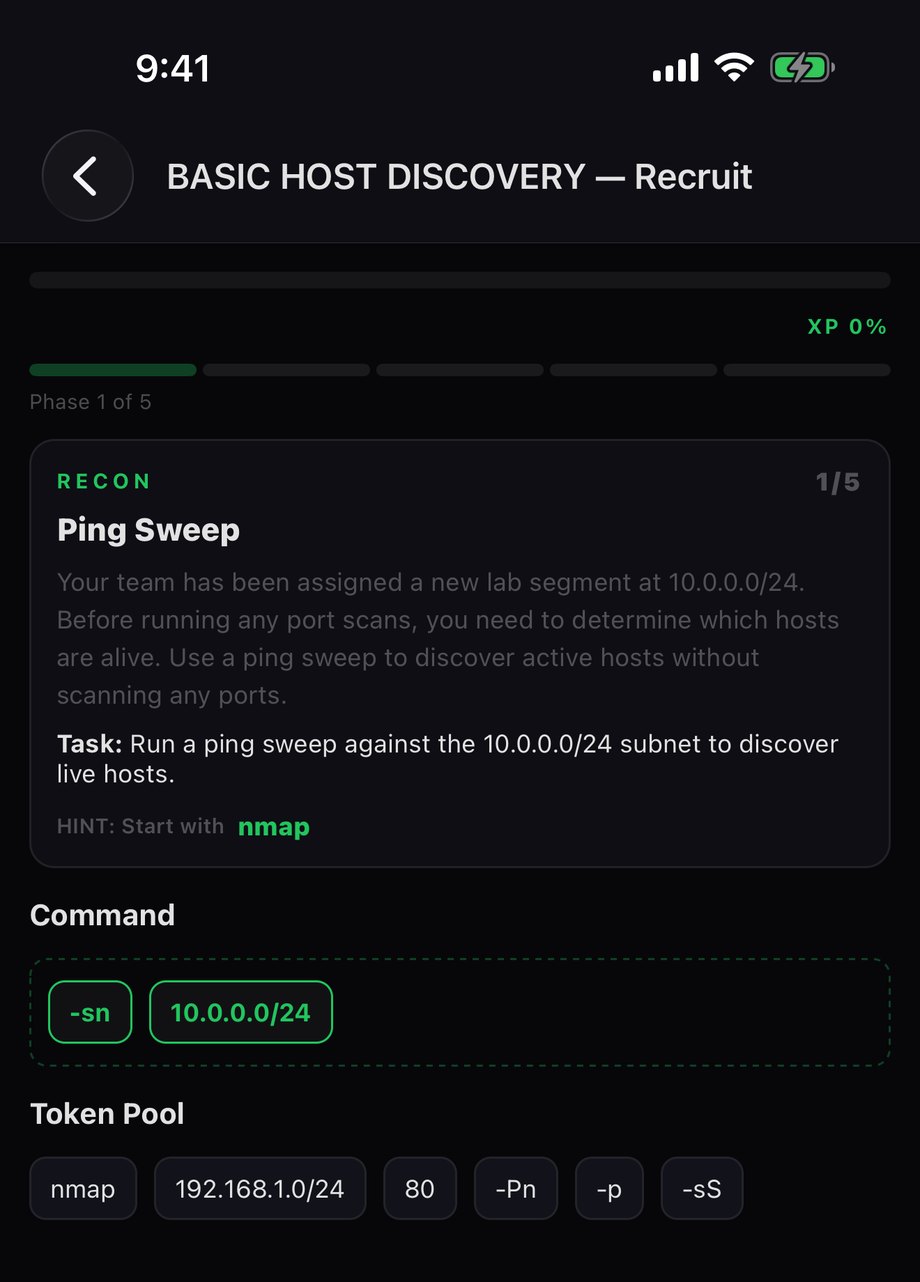
Rebuild the real command
Each mission is a breach broken into phases (recon, initial access, lateral movement, exfiltration, and so on). Every phase gives you an intel briefing and a pool of command tokens. You assemble them into the command that was actually run.
Read the intel
A short briefing sets the scene: what the operator knows, what they're after, and what's standing in the way.
Build the command
Tap tokens into the command slot in the right order. The wrong tokens are plausible distractors, so you have to know the syntax rather than guess.
Stay in the green
Red missions track your stealth and Blue missions track your detection coverage. Mistakes cost you, and too many gets you burned.
Four ways in
Learn the syntax
A free starter track for core command-line tools like nmap, curl, gobuster, hashcat, john, and hydra. XP-based with escalating hints and no stealth penalty. Built for beginners.
Think like the attacker
Exploitation, post-exploitation, web apps, Active Directory, wireless, and C2. Replay the operator's moves phase by phase while keeping your stealth up.
Respond like a defender
SIEM queries, network analysis, cloud, threat hunting, DFIR, malware and log analysis, incident response. Rebuild what should have caught the intrusion.
Full kill-chain replays
Complete campaigns reconstructed from published incident reports, playable from both sides: Emotet, Conti, Qbot, IcedID, LockBit, Bumblebee, and newer AI-era incidents like the 2025 Nx "s1ngularity" supply-chain compromise.
Real incidents, not hypotheticals
Campaigns are built from public sources such as The DFIR Report, CISA advisories, and published vendor incident write-ups. Every command and tool is reviewed against the tool's official documentation before release.
Study with purpose
Cert paths map GHOST missions onto each exam's domains. They track weighted progress by domain, flag your weakest area, and recommend the next module to play.
GHOST is an independent study aid and is not affiliated with or endorsed by any certification body.
Start free. Go deeper when ready.
Recruit
- Command-line fundamentals track
- A featured breach campaign each month
- Entry-level cert study paths
Operator
- The full Red, Blue, and Breach library
- All 11 cert study paths
- Every new monthly campaign drop
Pricing and any introductory offers are shown in the App Store at launch. No ads on any plan.
Your progress stays on your device.
GHOST v1 keeps your progress, stats, and leaderboard locally on your iPhone or iPad, with no account required to play. Questions, bug reports, or team and classroom interest: support@gil.consulting.
Help shape GHOST
We're looking for beta testers. If you'd like early access and a direct line to the people building GHOST, email beta@gil.consulting, or use the form if you'd rather not open your email app.
- Tell us which device you'll test on.
- We'll reply with an invite (TestFlight on Apple devices) when a spot opens.
- Test, tell us what breaks, and help decide what ships.
We use your details only to run the beta. See the privacy policy.